The framing of pirate IPTV services has undergone a subtle but significant shift in recent policy discourse. What was once solely a copyright-enforcement matter has become entangled with national security arguments, with advocacy groups now linking piracy platforms to the distribution of content by designated terrorist organisations. This reframing carries implications for how hosting providers, content networks, and regulators approach the problem.
The Mechanics of Pirate IPTV Distribution
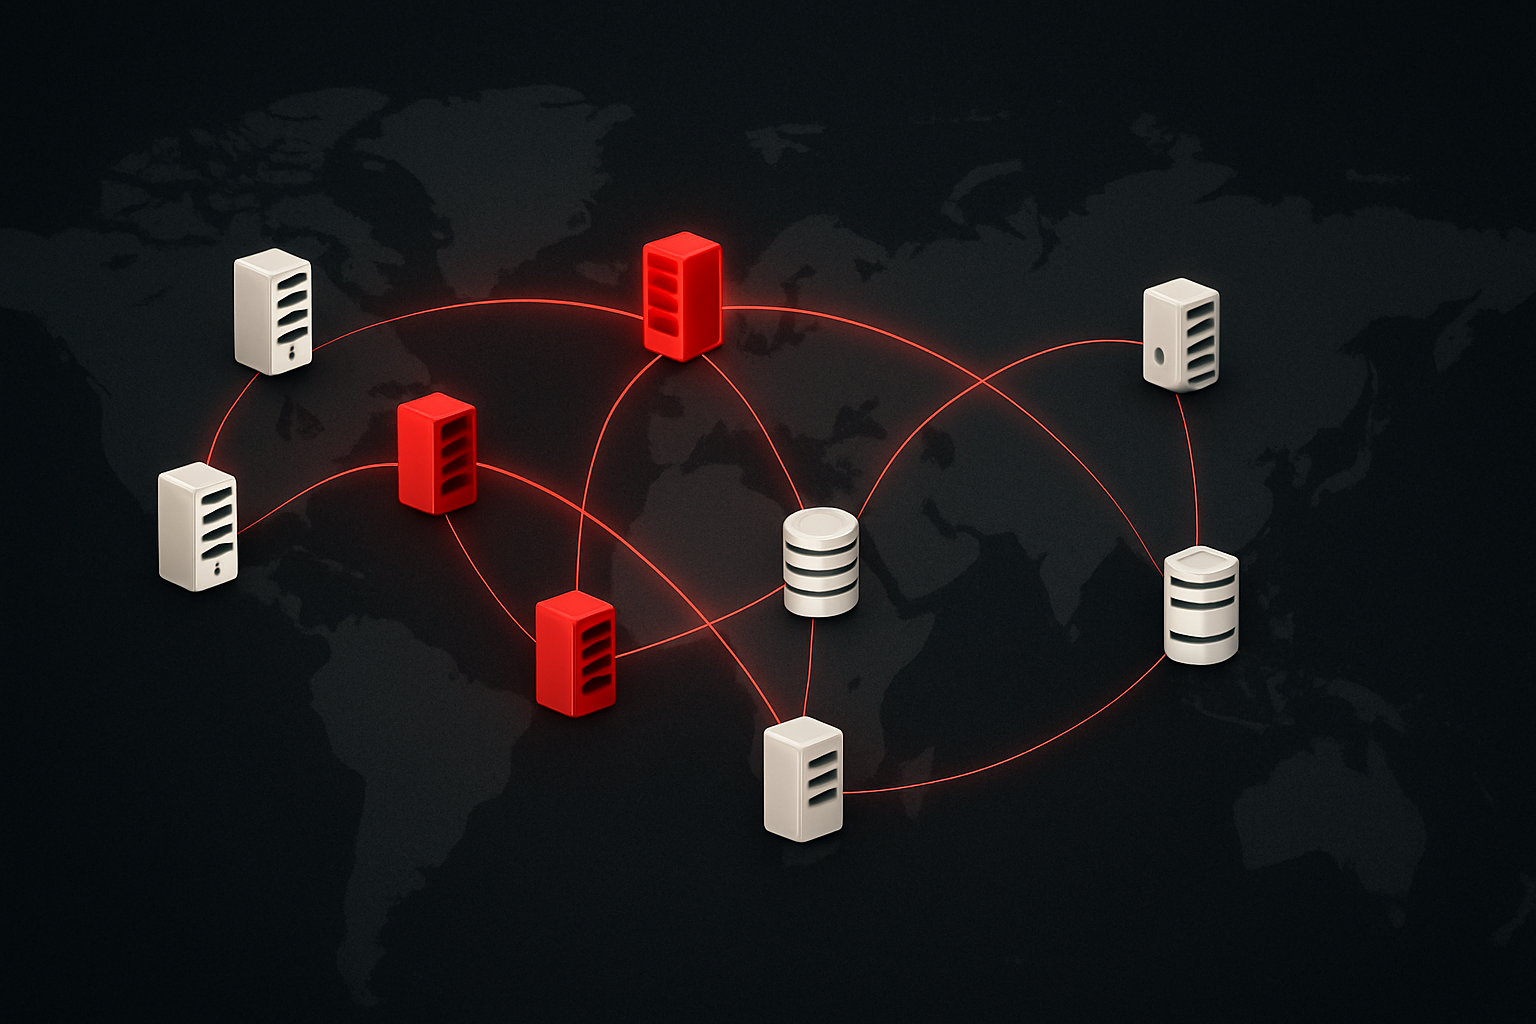
Pirate IPTV services operate as a hybrid between traditional broadcast infrastructure and on-demand streaming. They typically rely on a combination of distributed server resources, often hosted across multiple jurisdictions, to deliver live television streams and video-on-demand content. The architecture is relatively straightforward: a central playlist or Electronic Program Guide points clients to M3U streams or RTMP sources hosted on commodity servers or CDNs.
The hosting footprint for these services is fragmented intentionally. Primary infrastructure might exist in jurisdictions with weak copyright enforcement or ambiguous legal status around IPTV transmission. Secondary distribution uses fast-flux DNS, bulletproof hosting providers, or compromised legitimate servers. This distributed model makes takedown efforts labour-intensive and only temporarily disruptive.
From a technical perspective, IPTV piracy is straightforward to implement and remarkably resilient. A single provider can operate dozens of domains, mirror their content across geographically dispersed caches, and rotate infrastructure faster than legal action can proceed. The barrier to entry is low; the profit margins are substantial enough to justify ongoing infrastructure investment.
The National Security Argument and Its Mechanics
Recent policy interventions have attempted to reframe piracy as a vector for hostile state actors and designated organisations to reach Western audiences. The argument is that pirate IPTV platforms, by aggregating content from multiple sources without editorial oversight, inadvertently or deliberately carry propaganda channels alongside mainstream entertainment.
This framing opens a different policy avenue than traditional DMCA or copyright enforcement. National security rationales can justify DNS filtering, ISP-level blocking, or financial system restrictions without requiring copyright holders to prove infringement in each case. Recent reporting has highlighted these connections as justification for U.S. site-blocking legislation, which would delegate domain-level filtering authority to government agencies rather than courts.
From a hosting and infrastructure perspective, this shift matters significantly. It changes the legal and technical compliance burden on providers. A DMCA takedown targets specific content; a national security designation can affect entire services and all associated infrastructure, regardless of what proportion of their content is infringing or problematic.
Technical and Jurisdictional Implications
Site-blocking proposals typically rely on DNS filtering at the ISP level or upstream filtering at the registry or root nameserver level. This approach requires cooperation from network operators and telecommunications regulators. Technical implementation is straightforward but requires coordination across multiple entities.
The jurisdictional complexity lies in enforcement. Pirate IPTV services often register domains in jurisdictions with minimal compliance with U.S. sanctions or copyright law. Blocking at the DNS level is effective only in cooperating jurisdictions. International coordination remains limited, and domain operators can migrate quickly to alternative registries or top-level domains.
For hosting providers, the distinction between copyright enforcement and national security designation creates uncertainty. A provider hosting general-purpose infrastructure (VPS, CDN services) may find itself subject to blocking or delisting if customer content triggers national security concerns, even if the hosting itself is incidental to the service. This raises questions about provider liability, content responsibility, and the scope of what constitutes knowing facilitation of harmful activity.
The Broader Policy Landscape
The IPTV piracy debate sits at an intersection of copyright policy, national security, and technical regulation. Policymakers face legitimate concerns about both intellectual property protection and the distribution of content that violates sanctions regimes. The technical community faces pressure to implement filtering mechanisms that are difficult to make precise and easily subject to scope creep.
The argument that piracy platforms are security threats is not baseless, but it flattens a complex technical and legal problem into a single enforcement mechanism. Pirate IPTV services do exist on commodity infrastructure; some do carry problematic content; and yes, the economics reward providers indifferent to their customer base. But linking this to national security creates a template for blocking access to entire platforms based on the presence of designated content, rather than addressing the content distribution itself.
Site-blocking and DNS filtering are blunt instruments. They work at the domain level, not the content level. A pirate IPTV service that carries ninety percent mainstream content and ten percent problematic channels triggers the same blocking response as a service whose entire purpose is propaganda distribution. This binary approach may satisfy policy objectives, but it introduces collateral effects on legitimate services and raises questions about the durability of any enforcement regime that relies on DNS-level intervention alone.