When a critical load balancer sits in your infrastructure perimeter with no available patch, the options narrow quickly. Citrix NetScaler ADC and NetScaler Gateway deployments are currently facing exactly that scenario: two zero-day remote code execution vulnerabilities being actively exploited, with Citrix offering no published fix and no confirmed timeline for one.
The Exploitation Reality
Security researchers at watchTowr disclosed the active exploitation of these flaws on 26 September. The vulnerabilities affect NetScaler ADC and NetScaler Gateway appliances—devices that sit at the network edge, handling SSL termination, application delivery, and traffic routing for thousands of hosting providers and enterprises worldwide. Their position in the network stack makes them attractive targets; compromise them, and an attacker gains foothold access to downstream infrastructure.
Citrix's silence on the matter has left administrators in a holding pattern. Some have already made the difficult decision to take affected appliances offline rather than accept the exploitation risk. That choice carries its own cost: sudden service interruption, failover complexity, and operational strain.
Why This Matters for Infrastructure Operators
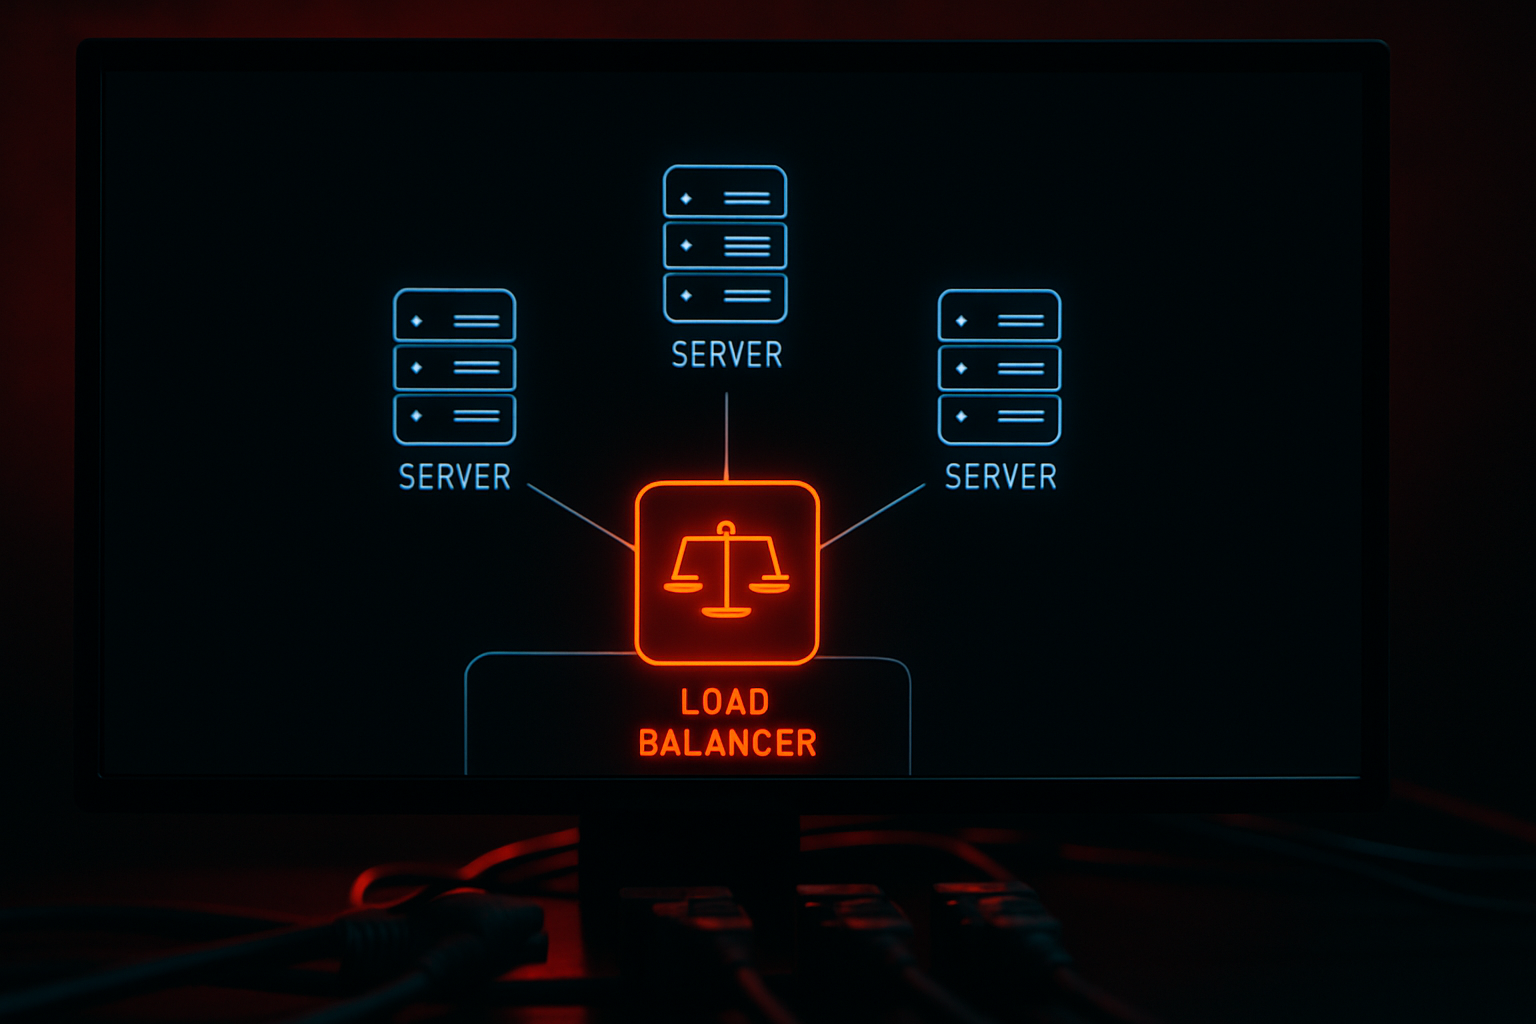
Load balancers are not merely convenience devices. They are trust boundaries. When deployed correctly, they terminate untrusted external connections, apply rate limiting, filter malicious payloads, and present a single SSL endpoint to the internet. An RCE vulnerability in that appliance grants an attacker direct access to your infrastructure's core routing layer.
From there, an attacker can observe internal traffic, redirect connections, harvest credentials, or pivot laterally into backend systems. For hosting providers managing multiple customer domains, a compromised load balancer could expose the entire customer base.
The zero-day nature compounds the problem. There is no patch to apply, no official workaround from the vendor, and no date when either will appear. Risk assessment becomes theoretical—you are managing uncertainty, not a known quantity.
Immediate Mitigation Options
Taking appliances offline is one extreme. More nuanced approaches include network segmentation and access controls. If a NetScaler appliance must remain in service, operators should restrict administrative access to trusted IP ranges, disable unnecessary features, and monitor for anomalous traffic patterns or unexpected connections to management interfaces.
Some infrastructure teams have implemented temporary reverse-proxy solutions using alternative load balancing software—nginx, HAProxy, or cloud-native ingress controllers—to absorb traffic while waiting for clarity from Citrix. This introduces complexity but reduces exposure during the vulnerability window.
Another layer of defence is behavioural monitoring. Even if you cannot patch the vulnerability itself, you can watch for exploitation attempts: unusual process spawning, unexpected outbound connections, or administrative API calls from unfamiliar sources. An intrusion detection system tuned to your NetScaler baseline can alert before damage occurs.
The Vendor Response Gap
This incident highlights a structural problem in infrastructure security. Unlike operating systems or web browsers, appliance firmware releases often move slowly. NetScaler deployments in large environments may run versions months or years old, not because administrators are negligent, but because updating a load balancer requires maintenance windows, failover testing, and careful staging.
When a zero-day appears and the vendor offers no patch, administrators have no good option. Waiting risks exploitation. Moving to alternative software requires engineering time and carries deployment risk. Taking services offline is economically painful.
Citrix's eventual response—when it comes—will likely include a patch and possibly recommendations for temporary configurations. Until then, infrastructure teams must treat their NetScaler appliances as potentially compromised and design defences accordingly. Consider this a reminder that perimeter devices require layered protection, not blind trust.